A dental phone system access audit should answer a simple question: can every identity, permission, and integration be tied to a current business need? Phone platforms may hold routing controls, call metadata, recordings, voicemail, exports, and account-recovery methods. A former employee or forgotten integration can affect both privacy and continuity.
Review access quarterly and after staffing, vendor, location, or ownership changes.
Build the complete identity inventory
Export user and administrator lists when the platform supports it. Then add identities that may not appear in the ordinary user screen:
- account owners and billing contacts;
- super administrators and location administrators;
- agents, shared lines, and desk phones;
- API keys, applications, and integrations;
- support or vendor access;
- recording, voicemail, and transcript permissions;
- export and reporting roles;
- number-porting and routing authority;
- recovery email addresses and phone numbers.
Compare this inventory to the practice's roster and vendor list. The phone-responsibilities guide can map each permission to an accountable role.
Test necessity, not seniority
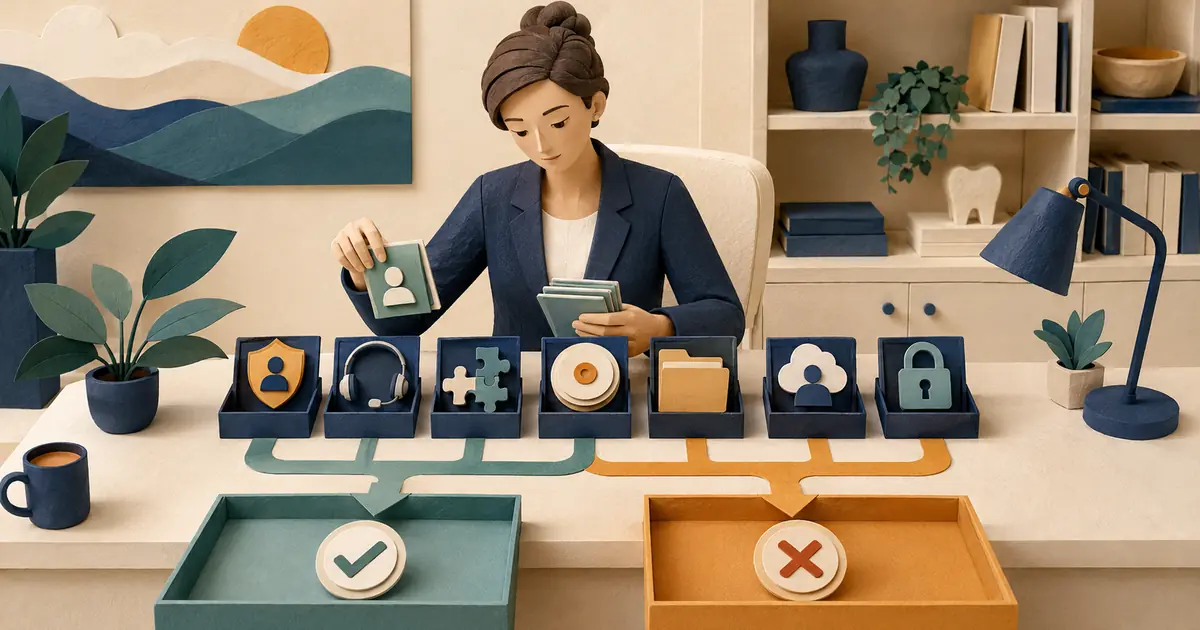
For each identity, record the owner, job responsibility, permission, approving person, last review, and removal condition. A manager does not automatically need every technical permission. A support vendor does not automatically need standing access.
Use these review decisions:
| Decision | Meaning |
|---|---|
| Retain | Current owner and business purpose confirmed |
| Reduce | Identity remains but excessive rights are removed |
| Suspend | Need is uncertain; preserve evidence while blocking use |
| Remove | No current authorized purpose |
| Investigate | Activity or ownership cannot yet be explained |
Do not delete evidence needed for an incident or legal hold. Coordinate with the practice's privacy, security, and legal procedures.
Eliminate shared administrative credentials
Shared administrator accounts weaken accountability and complicate offboarding. Where the system allows it, use unique identities, appropriate authentication, and role-based permissions. Store emergency recovery materials through an approved practice-controlled process, not a personal browser profile.
Review the receptionist-turnover plan whenever an employee leaves. Offboarding should cover call queues, voicemail, forwarding, mobile applications, exports, saved sessions, and provider support contacts—not just email.
Review data paths and secondary copies
Access is not limited to the phone console. Trace where call data goes: email notifications, downloaded spreadsheets, recording storage, transcription tools, analytics platforms, help-desk tickets, and backups.
For every path, document:
- purpose and data elements;
- receiving organization or system;
- authorized roles;
- authentication and audit evidence;
- retention and deletion owner;
- incident and contract contact;
- how the connection is disabled.
HHS risk-analysis guidance emphasizes an accurate and thorough assessment of potential risks and vulnerabilities to electronic protected health information. Apply that review to the practice's actual environment with qualified support; a checklist alone is not a compliance determination.
Sample activity and test removal
Review a defined sample of administrator changes, exports, forwarding edits, and failed sign-ins. Investigate activity outside normal duties or from unexplained identities. Keep the review proportionate and avoid turning it into employee surveillance.
At least once per cycle, test the offboarding procedure with a synthetic account. Confirm that sessions, tokens, mobile access, voicemail, routing authority, and recovery options are removed while required operations continue.
The phone and voicemail privacy guide can inform disclosure and storage controls.
Close the audit with evidence
An audit is complete when every exception has an owner, due date, corrective action, and verification result. Record who approved retained privileged access. Carry unresolved items forward visibly instead of marking the review complete because the meeting ended.
Missed Calls Dental boundary
Missed Calls Dental can provide access and handoff controls within its supported environment, but the practice owns its wider phone system, workforce authorization, vendor relationships, devices, and compliance program. It does not diagnose, verify insurance, or independently change appointments. SMS is separate and readiness-gated.
Amelia Brooks is an editorial pen name. This article was reviewed for accuracy and alignment with Missed Calls Dental product information.